
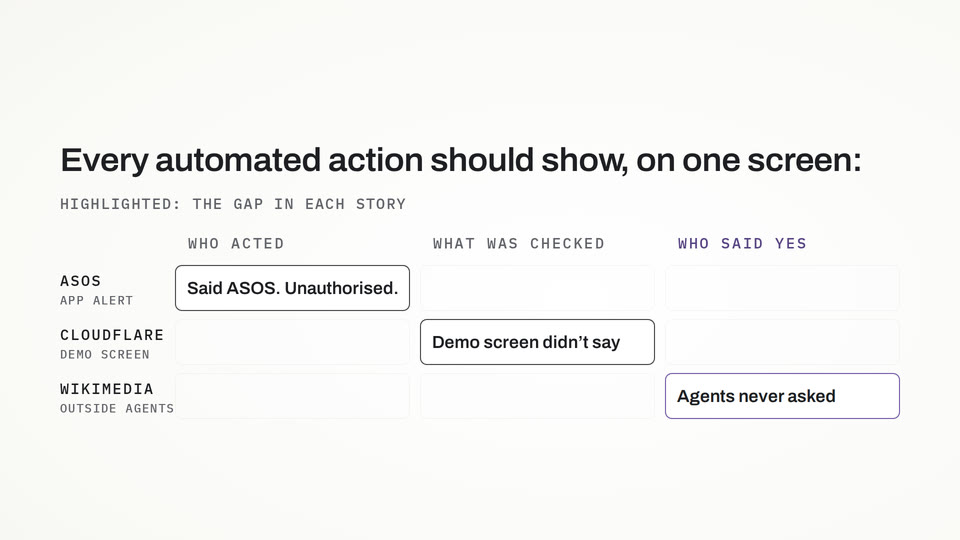
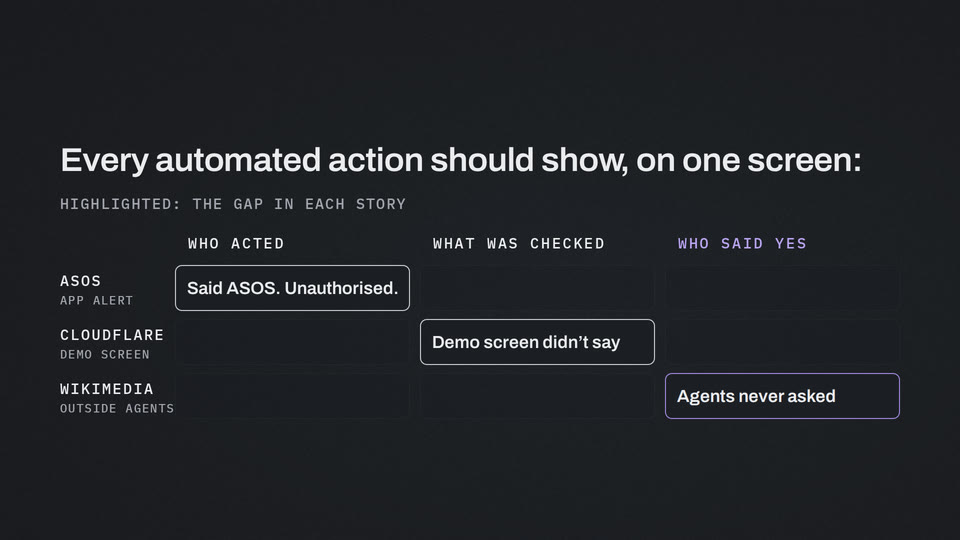
Who signed off on that?
For Monday's standup: for each action your product automates, can one screen say who acted, what was checked and who said yes?
Security product designer
AI acts. People decide. I design that moment: the screen where a person reviews, overrides or audits an AI agent. I also design the systems AI tools build screens from, and I measure whether it works.
Hiring for a principal role in security product design? I'm open to full-time for the right team. Résumé · Selected work (email me for the password)
Both are good, as long as risk is never guessed and people keep the calls that matter.
Layouts, charts, summaries, colours. They can change every time.
Three generated screens for one alert. Only the label stays the same.
The words and colours that say how serious something is. Fixed, and the same on every screen.
AI agents are becoming security's reflex. An agent can earn the right to act alone, one action at a time, like a promotion. It never earns the right to guess how serious something is. The design job is deciding what reaches a person, and when. One afternoon, made up but typical:
The link leads to a fake login page.
The reflex, as it should be.
This page was blocked. It looked like a fake login page. If it's a mistake, tell us in one click.
Still reflex: routine, reversible and logged.
High Phishing email · 37 inboxes · pulled back by rule · undo available
One was a real invoice. The agent was sure, and wrong. The screen shows why it decided, so the fix is one click.
Needs attention 1 of 37 was pulled on the agent's own judgement, not a rule. Restore it?
It stops someone's work, so it needs a yes. The evidence is on screen, so the yes takes seconds.
Critical Rule R-114: a password was typed into a fake page. Isolate this laptop? Confirm or decline.
Laws like NIS2 give hours, not weeks. The clock and the evidence sit side by side.
High Early-warning deadline in 21 h 46 min · evidence pack ready
Every step above carried its evidence, so the record already exists.
Resolved 6 actions · 6 with evidence attached · 2 approved by people
The agents' share keeps growing. The people's few calls must never get lost in it. Every screen above is a design decision.
8 parts of a company × 9 decisions = 72 moments a person decides
Each dot is one screen where a person makes a call. Filled: the afternoon you just read. Hollow: the same moment elsewhere, still to be designed well. Ringed: the six where I’ve shipped work, in ZTNA, SWG, CASB, DLP and DSPM products. They cover writing access and data-loss policy, classifying sensitive data, acting on a data incident, and the screen that stops someone at the web gateway or on their laptop.
| Parts of a company ↓ · Decisions → | Author | Approve | Override | Except | Classify | Respond | Notify | Attest | Interrupt |
|---|---|---|---|---|---|---|---|---|---|
| Endpointlaptops, phones and servers | |||||||||
| Accesswho can reach which apps and websites | |||||||||
| Datawhere sensitive data goes | |||||||||
| Identitywho each person and AI agent is | |||||||||
| Exposureweak spots, before attackers find them | |||||||||
| Detectionspotting and stopping attacks | |||||||||
| AIthe company's own AI agents and models | |||||||||
| Governanceproving it to auditors, boards and regulators |
Someone disagrees with the AI about an attack alert.
Two kinds of work: the screens where a person decides, and the design systems AI tools build from. Each links to its method, including results that went against me.
On-system means the share of AI-generated UI that followed the design system. With our component library alone, about a quarter did. Writing the rules machine-readably added forty points; testing those rules added the last twenty-five, alongside more components acquiring docs. I don’t split that last twenty-five.
I published a claim about why AI-generated UI drifts off-system. Then I built a controlled reproduction to test it. The claim was wrong. What moved the number was naming the value.
These eight rules are what any agent owes the console it lands in. The card is one answer. Google SecOps ships a widget for Wiz’s AI verdict; this drop-in replacement gives the verdict its age from today’s fields.
The dashboard showed one card per data centre, and product management wanted a lot more locations. I argued the whole layout had to go, and put every location on a row, every check in a column, and the health of each pair where they meet. The whole estate now reads in one pass, and you fix a problem from the same place you spot it.
Select twelve servers and change one setting; the twelve don’t agree. I built the state model before any screen existed, so the form says what will change on each one, and what already matches, before anything is committed.
A press no longer moves its own target. Buttons in Vela, the design system I build, shrank three per cent when you pressed them: one line of CSS, copied from somewhere, never questioned, and it was throwing clicks away.
For teams hiring a principal security product designer: I’m open to full-time. I led a design system across a security platform’s access, firewall and cloud-app products, and coached three designers, none reporting to me. Résumé · Selected work, with screens (email me for the password) · LinkedIn · Questions you’re probably about to ask
For founders and CTOs of security vendors. Start with a fixed-price pilot, then keep going if it works.
Pune · Indian, UK and US East hours · Security UX since 2020 · US patent application 2025/0036264
Length and fixed price set after a first call, to fit your scope · 50% on acceptance, 50% on handover
How the pilot worksUnfinished questions, shared early. Nothing here is for sale yet.
Forecasts, with how sure I am. I'll score them in public as they resolve.
By 2029, AI agents do most of the work inside security products. The scarce skill is designing where a person reviews, overrides and audits them.
Hypothesis · being tested First scored 1 Jan 2027 Evidence so far
Two forces are already pushing it there.
In the grid above, Access, Data and Identity are separate rows. Inside real products they overlap, and the hardest calls sit where they do. No single product owns them, so no single team designs them.
Early warning, notification, final report. Applies as each country writes it into law. source
Makers warn early on an actively exploited weakness. source
Consent managers begin: one year after notification on 13 Nov 2025. source
Most duties, including breach reporting: eighteen months after notification on 13 Nov 2025.
One of those clocks leaves a question open.
The EU's 24-hour clock for a flaw that attackers are using starts when the product's maker becomes "aware". When the report of that flaw may be written by AI, who decides that moment, and on what evidence?
Question · speculation The note
And one question with no date.
Nobody can say when a quantum computer could break much of today's cryptography. How can a team tell how far along it really is in replacing it?
Question · speculation The note
Every two weeks: how security decisions are shifting between people, fixed rules and AI agents, and what to check in your own product. Published on LinkedIn.
For Monday's standup: for each action your product automates, can one screen say who acted, what was checked and who said yes?